
On-Demand Webinar
How to Balance NERC CIPv6 vs. CIPv5 Compliance (and Why it Matters)
Mon, 08/15/2022
The extension of the NERC CIPv5 deadline to July 2016 means that registered entities have gained a small window of time for their compliance projects, but they now face a combined compliance deadline for CIPv5 and CIPv6 in July.
Join Nick Santora, CEO of Curricula, and Tim Erlin, Director of IT Risk & Security Strategist at Tripwire, for a discussion on the potential impact of CIPv6 on your...
Blog
Guarding the Grid: Navigating the Current and Future Landscape of Utility Cybersecurity
By Travis Emerson on Mon, 11/27/2023
Tripwire recently held its annual Energy and NERC Compliance Working Group. This year's attendees included more than 200 Tripwire customer utility personnel representing over 80 different registered entities from all across the US and Canada. The company sizes ranged from public utility districts and city municipalities to medium and larger-sized...
Demo
Fortra’s Tripwire for SOX Compliance
Tripwire: A Trusted Leader in SOX Compliance Automation The Sarbanes-Oxley Act requires that publicly held companies use internal controls for financial reporting. This mandate is incredibly difficult to meet using manual efforts, and Tripwire is here to help you automate SOX compliance — along with your other compliance requirements — to save your organization untold hours of work and costs...
Datasheet
NERC CIP Best Practices: The Tripwire Approach
Industrial operators subject to the North American Electric Reliability Corporation Critical Infrastructure Protection (NERC CIP) standard know that achieving compliance is no minor feat, and serious strategic consideration is required to ensure efficient resource use in the compliance process. By meeting NERC CIP compliance, these companies take important steps towards securing their IT/OT...
Datasheet
Why Energy Utilities Can Count on Fortra’s Tripwire
As an energy industry professional, you understand the consequences of subpar protection and the need for reliable, iron-clad security controls. Evaluating new cybersecurity software to protect your energy environment shouldn’t involve guesswork, especially when you are trying to match capabilities to your particular needs. This datasheet provides a quick view of Tripwire’s energy solution. See...
Datasheet
Tripwire NERC CIP Executive Brief
North American electric utility companies constantly balance the need to be audit-ready for NERC CIP compliance against their top priority: ensuring the reliability of the bulk electric system.NERC CIP compliance, especially when approached using manual methods, is complex, time-consuming, and prone to human error. Further, NERC CIP requirements often infer security skill sets beyond those of many...
Datasheet
Achieving Resilience While Fulfilling NERC CIP Requirements
Some of our nation’s most critical physical infrastructure is represented by the national Bulk Electric Systems (BES). Today’s digital world relies upon this interconnected network of power generation and transmission systems more than ever. To ensure the reliability and resilience of that network, providers must continually manage threats to the infrastructure, including many that relate to...
Datasheet
The Tripwire NERC CIP Solution Suite
The North American Electric Reliability Corporation (NERC) maintains comprehensive reliability standards that define requirements for planning and operating the bulk electric system (BES). Among these are the Critical Infrastructure Protection (CIP) Cyber Security Standards, which specify a minimum set of controls and processes for power generation and transmission companies to follow to ensure...
Datasheet
Tripwire Allowlisting
Changes occur nearly every second in the typical network. These changes most commonly include those made to group memberships, which ports are open, software patches, and other categories. That is precisely why it is so important to remain compliant with standards that regulate change monitoring, such as North American Energy Reliability Corporation Critical Infrastructure Protection (NERC CIP). ...
Datasheet
Tripwire and GDPR: Achieve Compliance Using Foundational Controls
The recently enacted European Union General Data Protection Regulation (GDPR) requires organizations to take adequate measures to ensure the security and privacy of personal data of any European citizen. This supersedes the previous Data Protection directive. As a regulation—as opposed to a mere directive—it directly imposes a uniform data security law regime on organizations that need to comply.
...
Datasheet
Automated TISAX Compliance
TISAX, the Trusted Information Security Assessment Exchange, is a mandatory compliance requirement for companies that touch any point of the German automotive supply chain. Its industry-wide enforcement applies to auto manufacturers and OEMs (original equipment manufacturers), but reaches further to encompass development and procurement departments as well: Even if your company isn’t Germany based...
Blog
Are Financial Services IT Pros Overconfident in Data Breach Detection Skills?
Fri, 01/29/2016
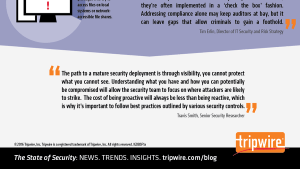
Tripwire studied confidence vs. knowledge of financial services IT security pros on seven key security controls necessary to detect a data breach. For many controls IT pros believed they had the information necessary to detect a breach quickly but provided contradictory information about the specific data.
...
Product Video
Watch a Demo of Tripwire Enterprise
Mon, 08/15/2022
Compliance frameworks are notoriously dense and complex, making them difficult to put into action. Compliance is also time-consuming—especially if you’re still attempting manual configuration of your systems, applications, databases and cloud assets. Manual configuration is error-prone and immediately out of date the moment an assessment ends. And a lack of compliance can result in failing audits,...
Blog
What you need to know about PCI 4.0: Requirements 1, 2, 3 and 4.
By David Bruce on Tue, 06/14/2022
The Payment Card Industry Security Standards Council has released its first update to their Data Security Standard (PCI DSS) since 2018. The new standard, version 4.0, is set to generally go into effect by 2024, but there are suggested updates that are not going to be required until a year after that. This, of course, creates a couple of problems...
Blog
What Is the ISA/IEC 62443 Framework?
By Michael Betti on Mon, 11/04/2024
Cybersecurity threats to manufacturing and process plants come from a wide range of attack vectors, including supply chain, logistics, enterprise computing, remote connections, operator stations, programmable logic controllers, distributed control systems (DCSs), smart sensors, and new smart devices. Internet of Things (IoT) technologies offer greater connectivity and endless applications, but...
Blog
CIS Control 16: Application Software Security
By Matthew Jerzewski on Wed, 10/23/2024
The way in which we interact with applications has changed dramatically over the years. Enterprises use applications in day-to-day operations to manage their most sensitive data and control access to system resources. Instead of traversing a labyrinth of networks and systems, attackers today see an opening to turn an organization's application against it to bypass network security controls and...